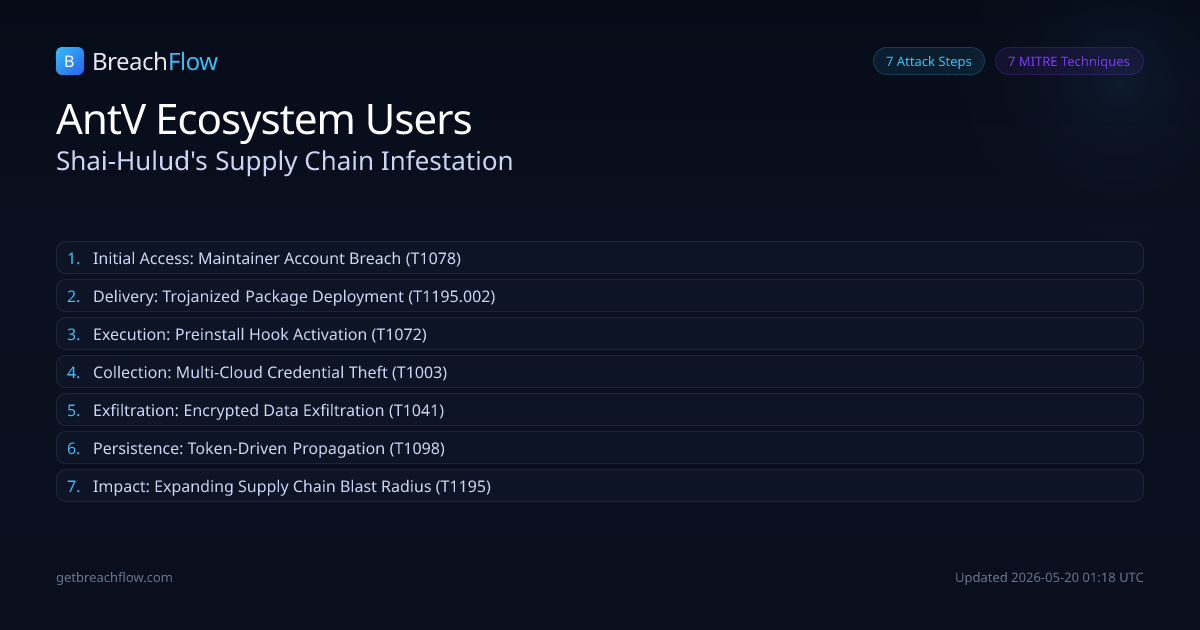
The Mini Shai-Hulud campaign, attributed to TeamPCP, compromised the 'atool' npm maintainer account to push 639 malicious versions across 323 unique packages in the @antv ecosystem. The malware steals over 20 types of credentials, including AWS, GitHub, and npm tokens, exfiltrating them to t.m-kosche[.]com:443 or via GitHub repositories.
Initial Access
Maintainer Account Breach
confirmed
Threat actors compromised the 'atool' npm maintainer account, gaining unauthorized access to publish new package versions within the @antv ecosystem.
Defender cut points
Enforce phishing-resistant FIDO2 MFA on all npm maintainer accounts.Implement strong password policies and regular credential rotation for critical developer accounts.