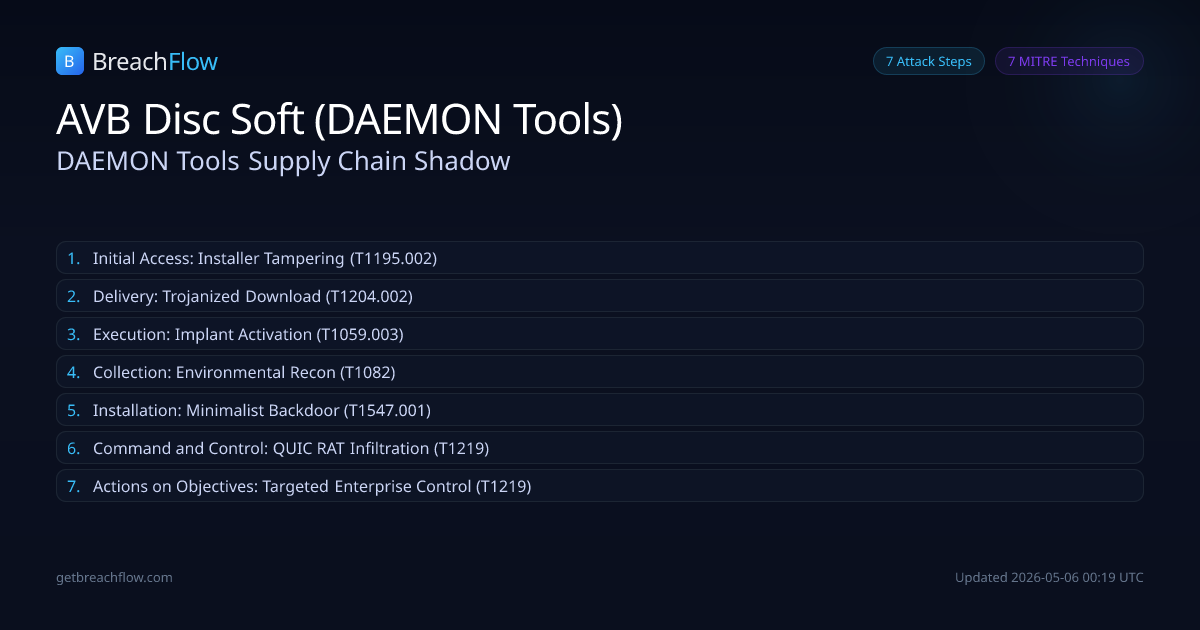
A supply chain attack compromised official DAEMON Tools installers (versions 12.5.0.2421 to 12.5.0.2434) with malware since April 8, 2026. The malicious payload included `envchk.exe` for system info collection, a minimalist backdoor (`cdg.exe`, `cdg.tmp`), and the QUIC RAT, impacting thousands globally and targeting specific organizations in Russia, Belarus, and Thailand.
Initial Access
Installer Tampering
confirmed
Attackers compromised the build or distribution process of DAEMON Tools, injecting malicious code into official installers (versions 12.5.0.2421 to 12.5.0.2434) and signing them with legitimate digital certificates.
Defender cut points
Implement robust software supply chain security measures, including code signing certificate protection and integrity checks for build artifacts.