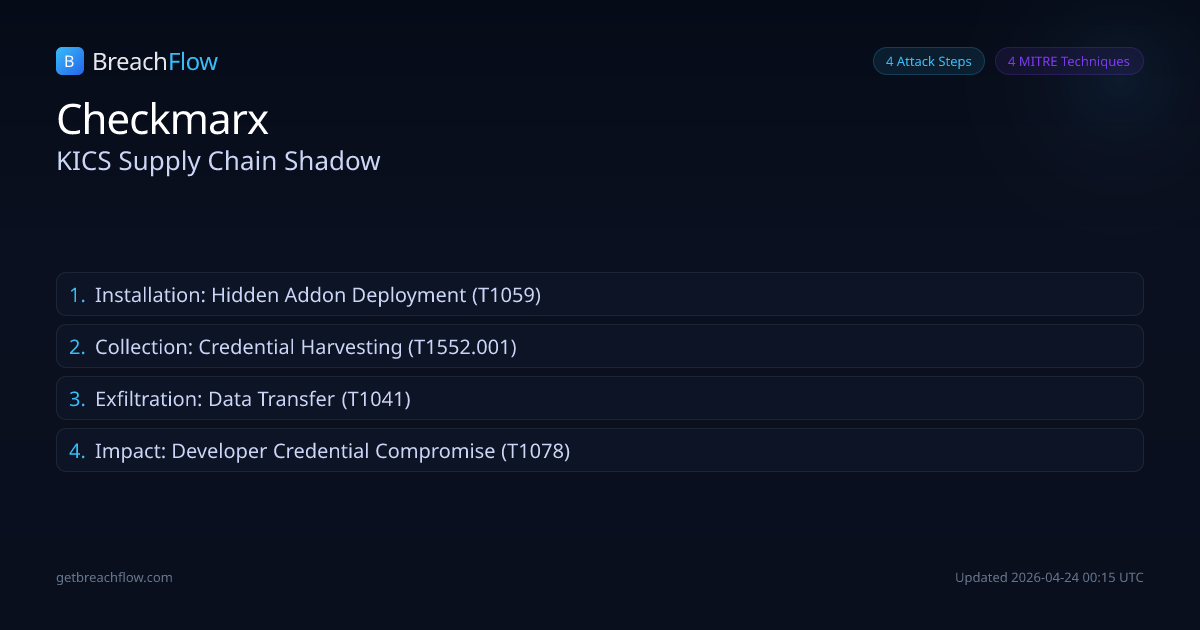
Hackers compromised Checkmarx's KICS analysis tool by injecting malicious code into official Docker images, VSCode, and Open VSX extensions. This led to the deployment of an 'MCP addon' malware designed to steal sensitive developer credentials and exfiltrate them to an impersonating domain.
Installation
Hidden Addon Deployment
confirmed
The compromised Docker images and extensions downloaded a hidden 'MCP addon' feature from a hardcoded GitHub URL. This addon contained a multi-stage credential theft and propagation component as 'mcpAddon.js'.
Defender cut points
Implement application whitelisting to prevent unauthorized script execution in development environments.Enforce endpoint detection and response (EDR) to detect suspicious file downloads and execution from development tools.