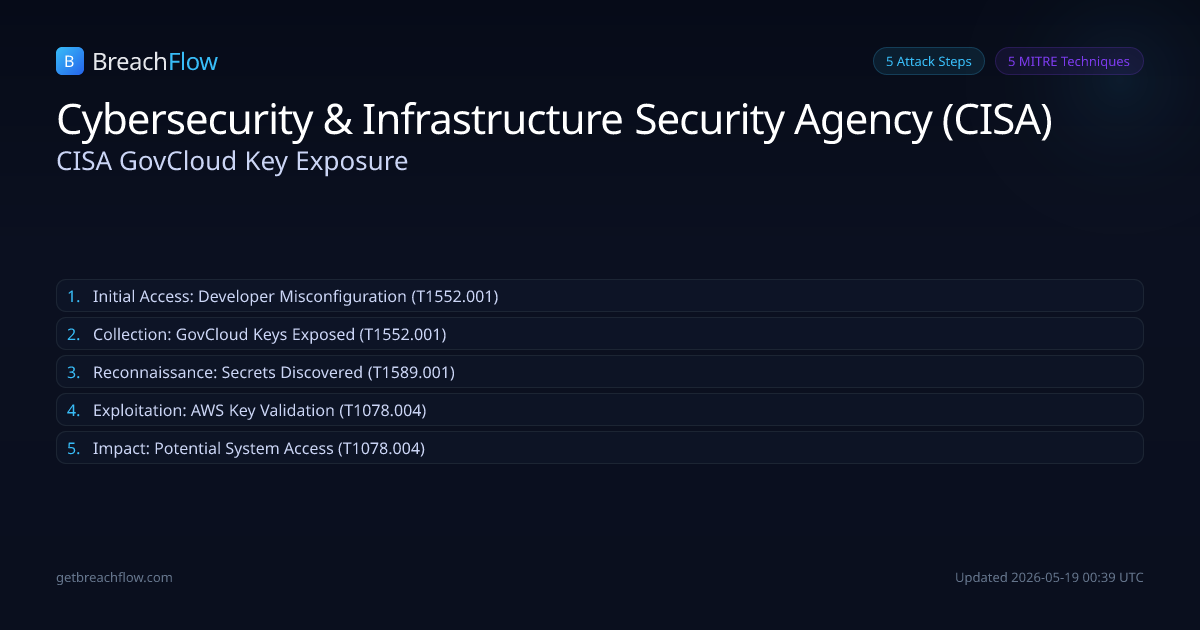
A CISA contractor publicly exposed highly privileged AWS GovCloud keys, plaintext passwords for internal CISA systems, and internal artifactory credentials on a GitHub repository. The repository, named 'Private-CISA,' also contained files detailing CISA's software build and deployment processes. While CISA states no sensitive data was compromised, security experts confirmed the validity of the exposed AWS keys.
Initial Access
Developer Misconfiguration
confirmed
A CISA contractor created a public GitHub repository named 'Private-CISA' and explicitly disabled GitHub's default secret detection feature, leading to the exposure of sensitive credentials.
Defender cut points
Implement automated secret scanning in CI/CD pipelinesEnforce policy to prevent disabling security features in source controlConduct regular security awareness training for developers on secure coding practices