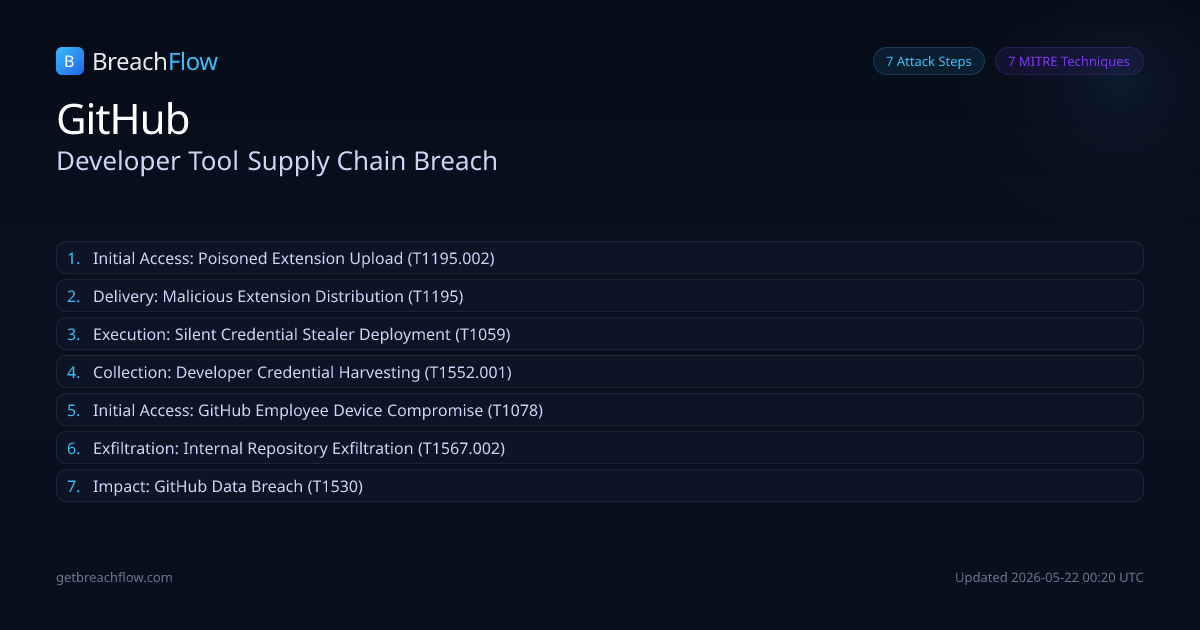
The cybercriminal group TeamPCP compromised GitHub's internal repositories by exploiting a poisoned Nx Console VS Code extension. The malicious extension, active for only 18 minutes, deployed a credential stealer targeting 1Password, Anthropic Claude Code, npm, GitHub, and AWS credentials from a GitHub employee's device.
Initial Access
Poisoned Extension Upload
confirmed
TeamPCP compromised a developer's system from the Nx team, leading to the upload of a malicious version of the Nx Console VS Code extension (nrwl.angular-console) to the Visual Studio Marketplace. This was part of a broader TanStack supply chain attack.
Defender cut points
Implement strict code signing and integrity checks for developer tools and extensionsEnforce multi-factor authentication for marketplace publishing accounts