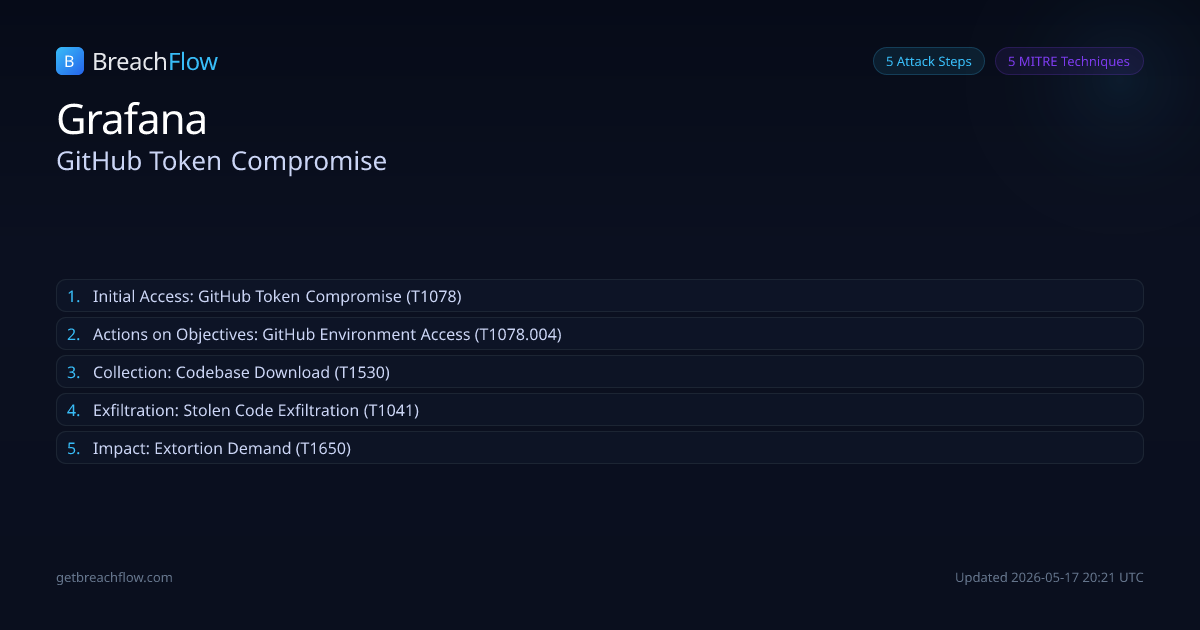
An unauthorized party obtained a token, granting them access to Grafana's GitHub environment and allowing the download of its codebase. The threat actor, identified as CoinbaseCartel, subsequently attempted to extort Grafana, demanding payment to prevent the stolen data from being published.
Initial Access
GitHub Token Compromise
confirmed
An unauthorized party obtained a token that granted them the ability to access Grafana's GitHub environment. The specific method of token acquisition was not disclosed.
Defender cut points
Implement strong credential management policies for API tokensRegularly rotate GitHub tokens and enforce least privilegeMonitor for unusual token usage patterns