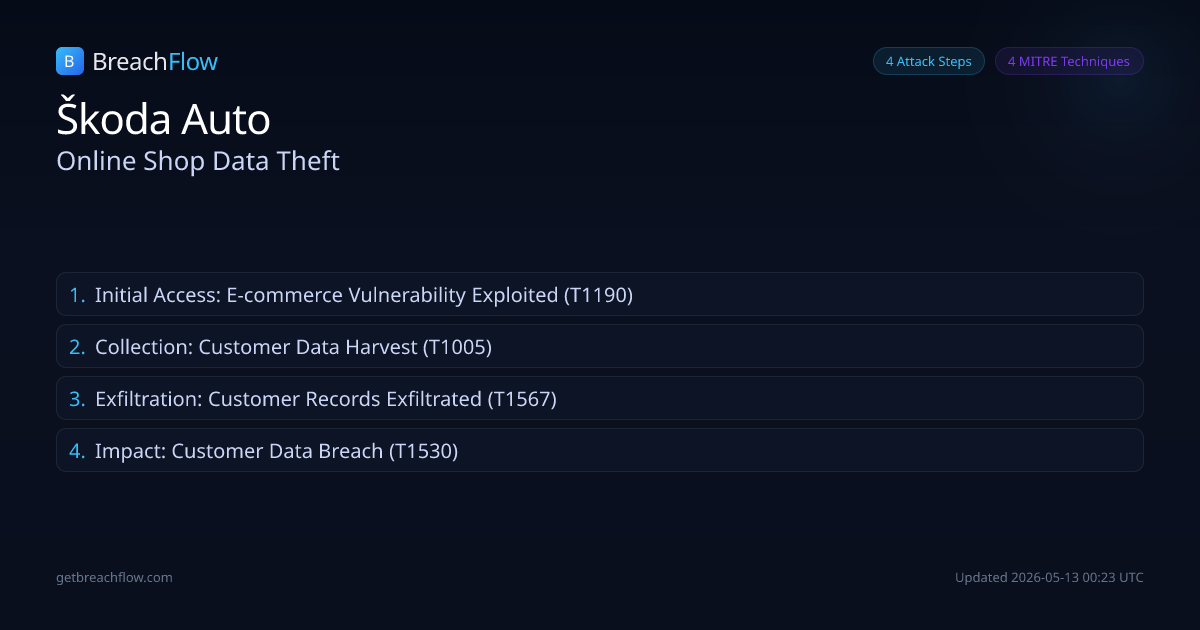
Škoda Auto, a Volkswagen Group subsidiary, disclosed a data breach after attackers exploited an unspecified vulnerability in its online shop software. Customer data, including names, addresses, contact information, order details, and hashed login credentials, was stolen. Financial information was not compromised.
Initial Access
E-commerce Vulnerability Exploited
confirmed
Threat actors exploited an unspecified vulnerability in the standard software of Škoda Auto's online store, gaining unauthorized access to the system.
Defender cut points
Implement regular vulnerability scanning and penetration testing for web applicationsEnsure timely patching and updates of all e-commerce platform software