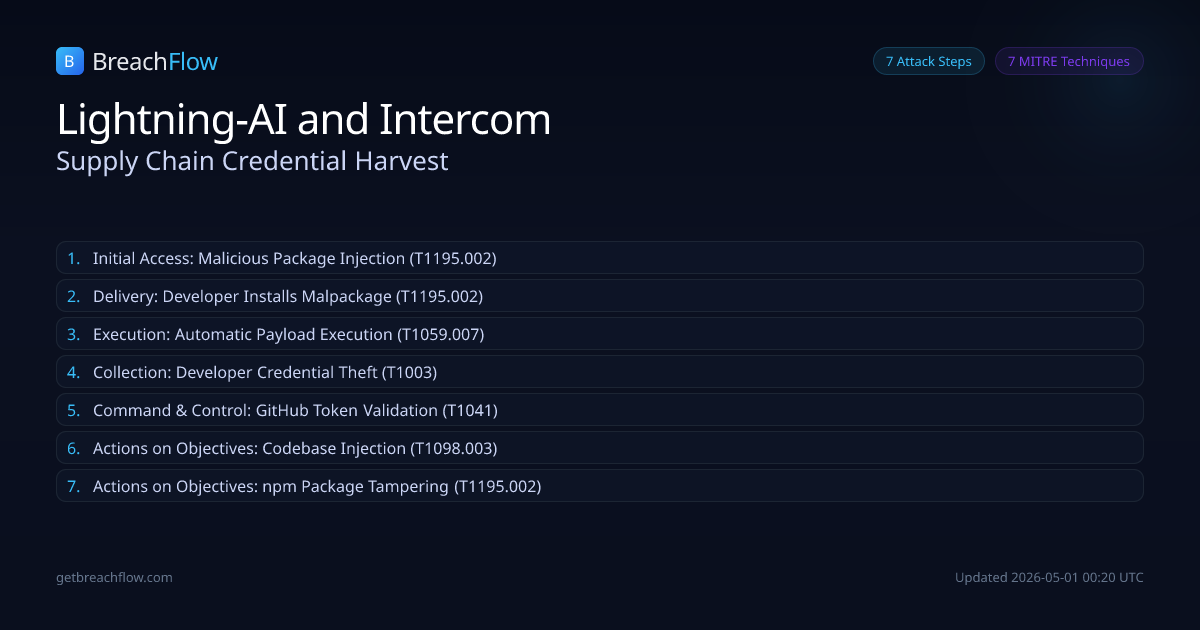
Threat actors, identified as TeamPCP, compromised the PyPI 'Lightning' package (versions 2.6.2 and 2.6.3) and the 'intercom-client' npm package (version 7.0.4) in supply chain attacks. The attack involved injecting obfuscated JavaScript payloads to steal developer credentials, including GitHub tokens, and propagate malware through developer environments.
Initial Access
Malicious Package Injection
confirmed
Threat actors compromised the PyPI 'Lightning' package (versions 2.6.2, 2.6.3) and the 'intercom-client' npm package (version 7.0.4), injecting malicious code. This was part of the Mini Shai-Hulud supply chain campaign.
Defender cut points
Implement robust CI/CD security, including package signing and integrity checks for published packages.Enforce strict access controls and multi-factor authentication for package repository publishing accounts.