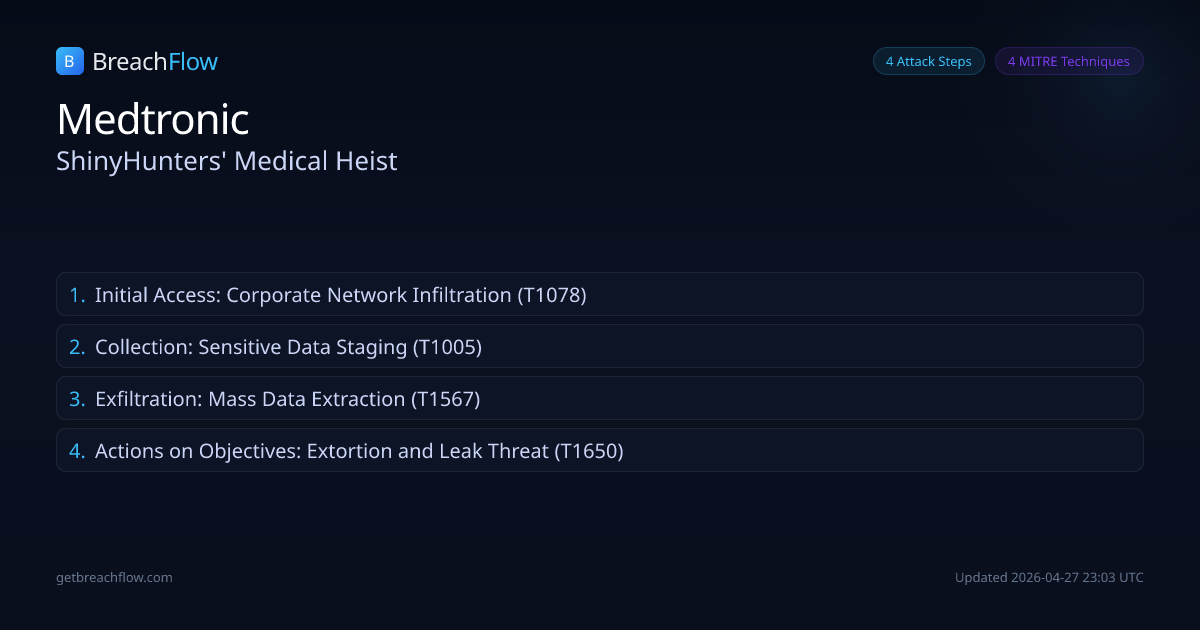
Data extortion group ShinyHunters breached Medtronic's corporate IT systems, claiming to have stolen over 9 million records containing PII and terabytes of internal corporate data. Medtronic confirmed the breach but stated no impact to products, patient safety, or manufacturing operations. The group threatened to leak the data if a ransom was not paid.
Initial Access
Corporate Network Infiltration
confirmed
Threat actors gained unauthorized access to Medtronic's corporate IT systems. The specific method of initial access was not detailed in the report.
Defender cut points
Enforce phishing-resistant FIDO2 MFA on all corporate accountsImplement robust network segmentation for critical IT systemsRegularly patch and update all internet-facing applications and systems