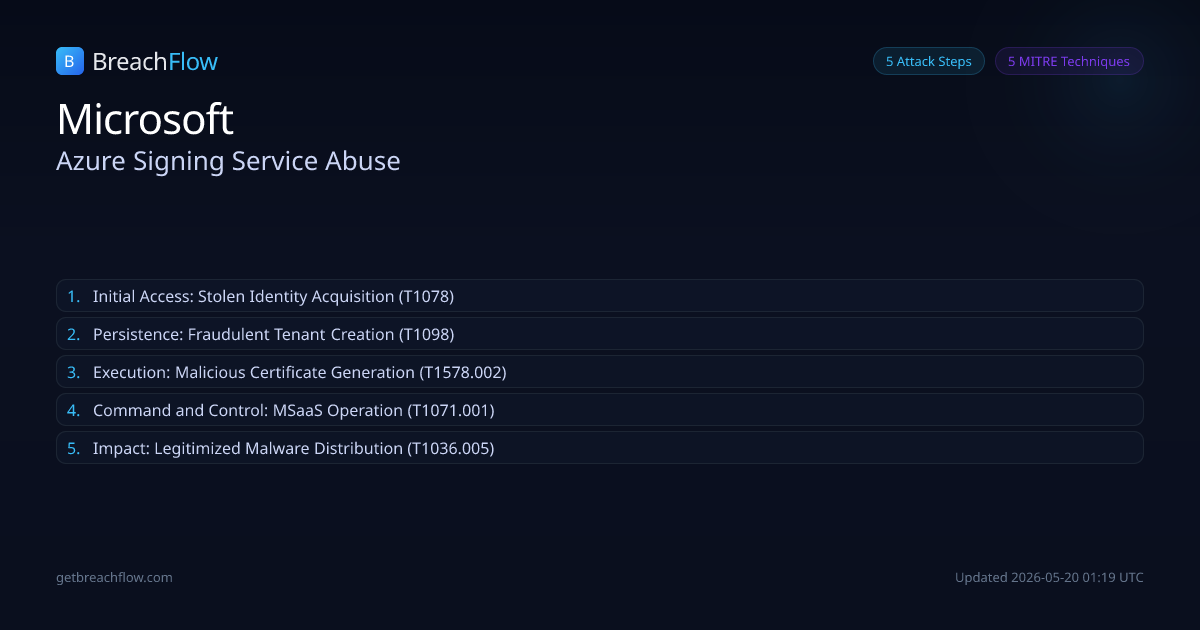
Microsoft disrupted Fox Tempest's malware-signing-as-a-service (MSaaS) operation, which abused the Azure Artifact Signing platform to create over 1,000 fraudulent code-signing certificates. This service, promoted on Telegram, generated millions of dollars and was used by ransomware gangs like Rhysida, Akira, and INC, as well as malware operations like Oyster, Lumma Stealer, and Vidar.
Initial Access
Stolen Identity Acquisition
likely
Fox Tempest likely used stolen identities from the United States and Canada to pass identity verification requirements for Microsoft's Artifact Signing service.
Defender cut points
Implement robust identity verification processes with multi-factor authentication for new account creation and certificate requests.