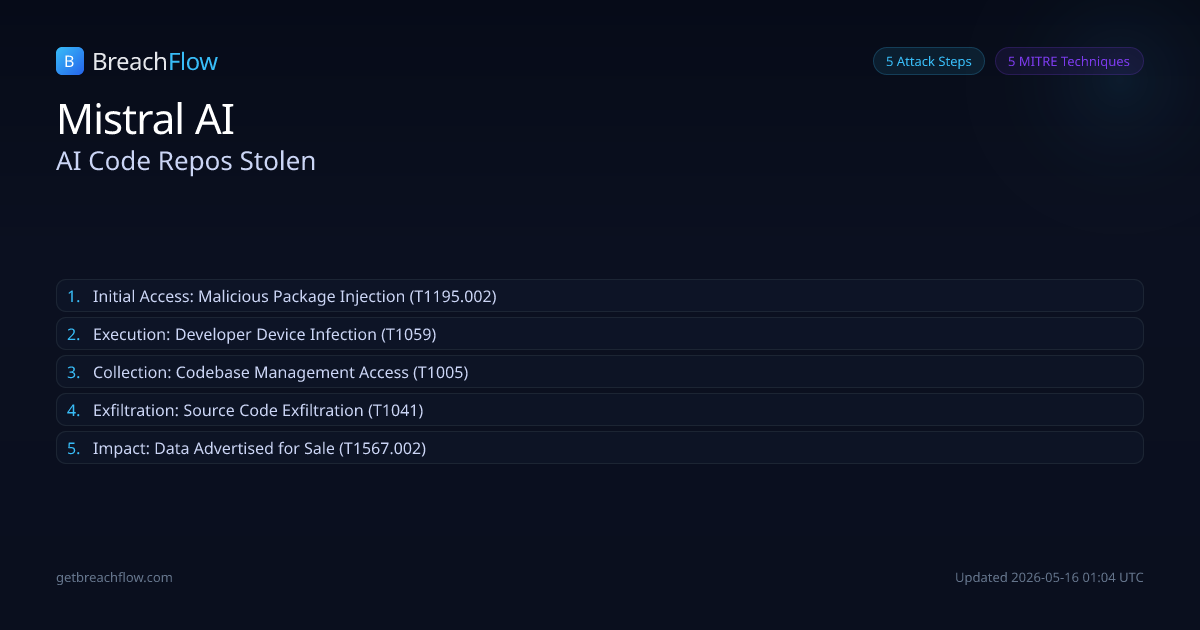
TeamPCP hackers compromised Mistral AI's codebase management system via a supply-chain attack involving malicious TanStack and Mistral npm packages. They exfiltrated nearly 5 GB of internal source code from 450 repositories and are now advertising it for sale for $25,000.
Initial Access
Malicious Package Injection
confirmed
The incident began with the compromise of official TanStack and Mistral AI packages through stolen CI/CD credentials and legitimate workflows, leading to the injection of malicious code into software dependencies.
Defender cut points
Implement strong access controls and multi-factor authentication (MFA) for CI/CD systems.Regularly audit CI/CD logs for suspicious activity and unauthorized changes.Utilize software composition analysis (SCA) tools to detect malicious or vulnerable dependencies.