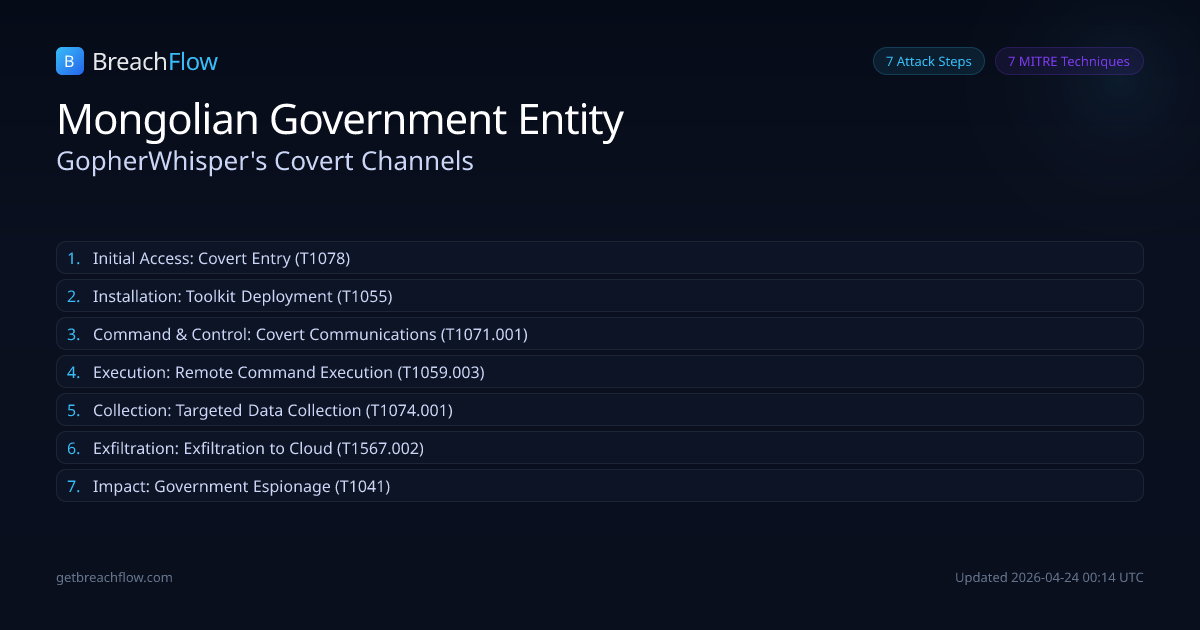
GopherWhisper, a Chinese state-backed APT group, utilized a custom Go-based malware toolkit, including LaxGopher, RatGopher, and BoxOfFriends, to compromise a Mongolian government entity. The group leveraged legitimate services like Slack, Discord, and Microsoft 365 Outlook for command and control, and exfiltrated stolen data using CompactGopher to File.io. ESET identified 12 compromised systems and recovered extensive C2 communications.
Initial Access
Covert Entry
likely
GopherWhisper likely gained initial access to the Mongolian government entity's network, enabling the subsequent deployment of their custom malware toolkit. The specific initial access vector is not detailed in the report.
Defender cut points
Implement robust endpoint detection and response (EDR) to detect anomalous login activities.Enforce phishing-resistant FIDO2 MFA on all user accounts.