Multiple Asian Governments, Poland, and International Consortium of Investigative Journalists (ICIJ)Shadow Earth's Global EspionageUpdated 2026-05-02 00:37 UTC
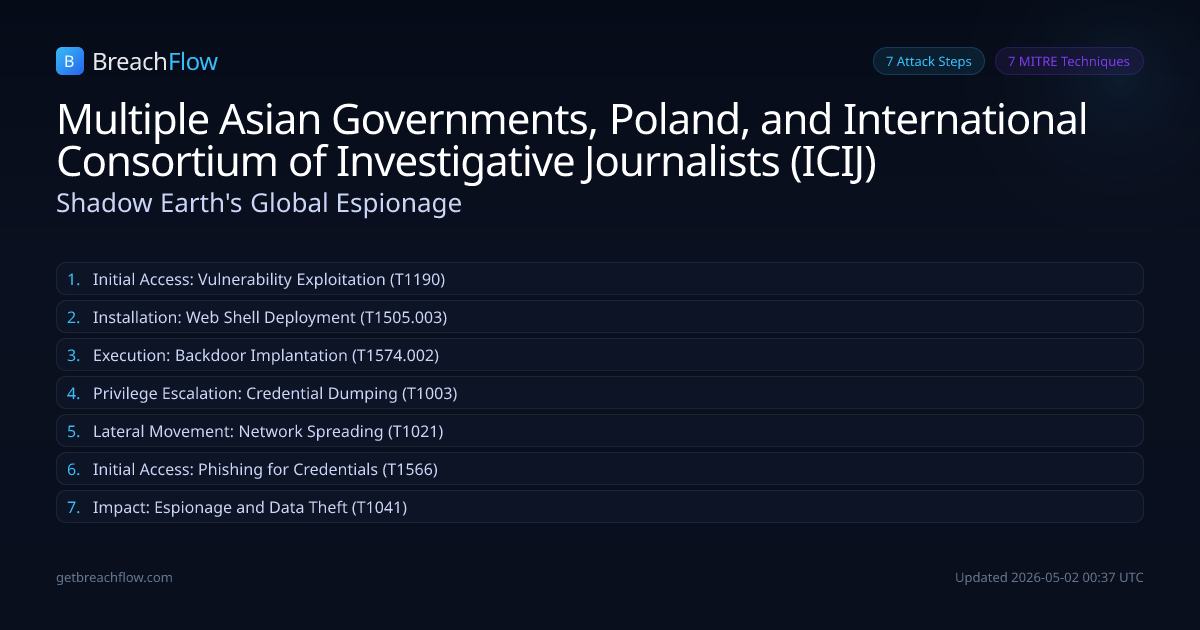
China-aligned threat actors SHADOW-EARTH-053, GLITTER CARP, and SEQUIN CARP conducted espionage campaigns targeting government and defense sectors in South, East, and Southeast Asia, Poland, and journalistic organizations like ICIJ. They exploited N-day vulnerabilities in Microsoft Exchange and IIS, deployed Godzilla web shells and ShadowPad/Noodle RAT backdoors, used Mimikatz for privilege escalation, and Sharp-SMBExec for lateral movement. Phishing campaigns were also used to harvest credentials from journalists and activists.
Initial Access
Vulnerability Exploitation
confirmed
SHADOW-EARTH-053 exploited N-day vulnerabilities in internet-facing Microsoft Exchange and Internet Information Services (IIS) servers, including the ProxyLogon chain and React2Shell (CVE-2025-55182).
Defender cut points
Apply latest security updates and cumulative patches to Microsoft Exchange and IISDeploy IPS/WAF with rulesets specifically tuned to block exploit attempts against known CVEs