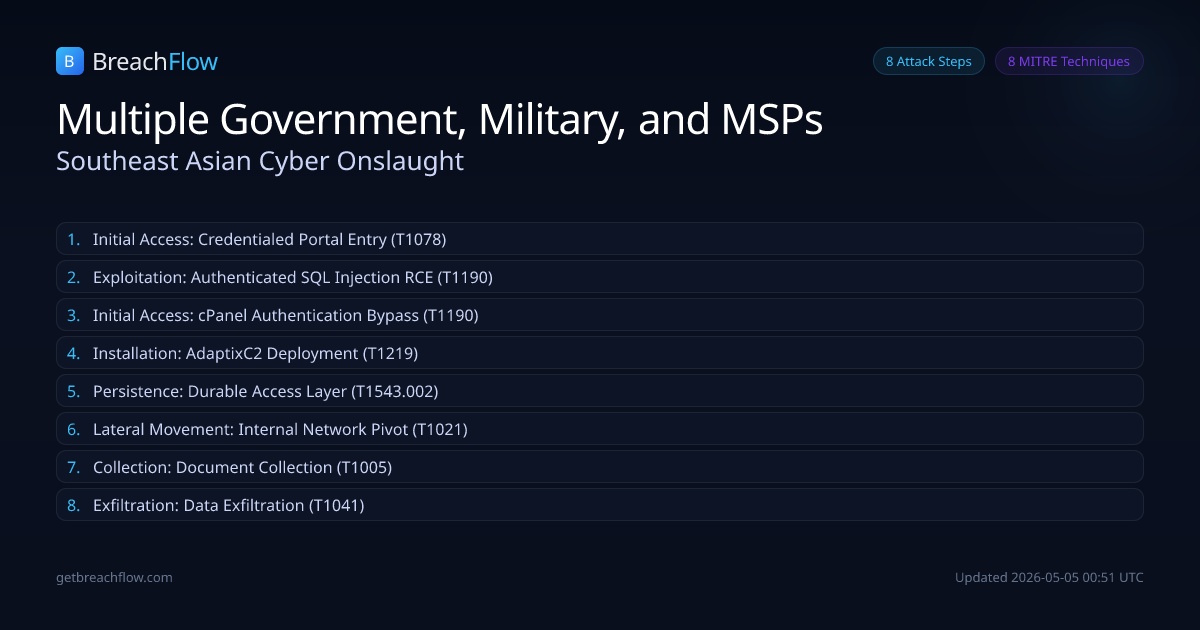
An unknown threat actor exploited CVE-2026-41940 in cPanel/WHM to target government and military entities in Southeast Asia, as well as MSPs and hosting providers globally. The actor also used an authenticated SQL injection and RCE against an Indonesian defense portal, deploying the AdaptixC2 framework, OpenVPN, and Ligolo for persistence and exfiltrating Chinese railway-sector documents.
Initial Access
Credentialed Portal Entry
confirmed
The threat actor gained initial access to an Indonesian defense sector training portal using valid credentials, bypassing CAPTCHA by reading server-issued session cookies.
Defender cut points
Enforce phishing-resistant FIDO2 MFA on all portal accountsImplement robust CAPTCHA solutions that cannot be bypassed via session cookiesMonitor for unusual login patterns and credential reuse