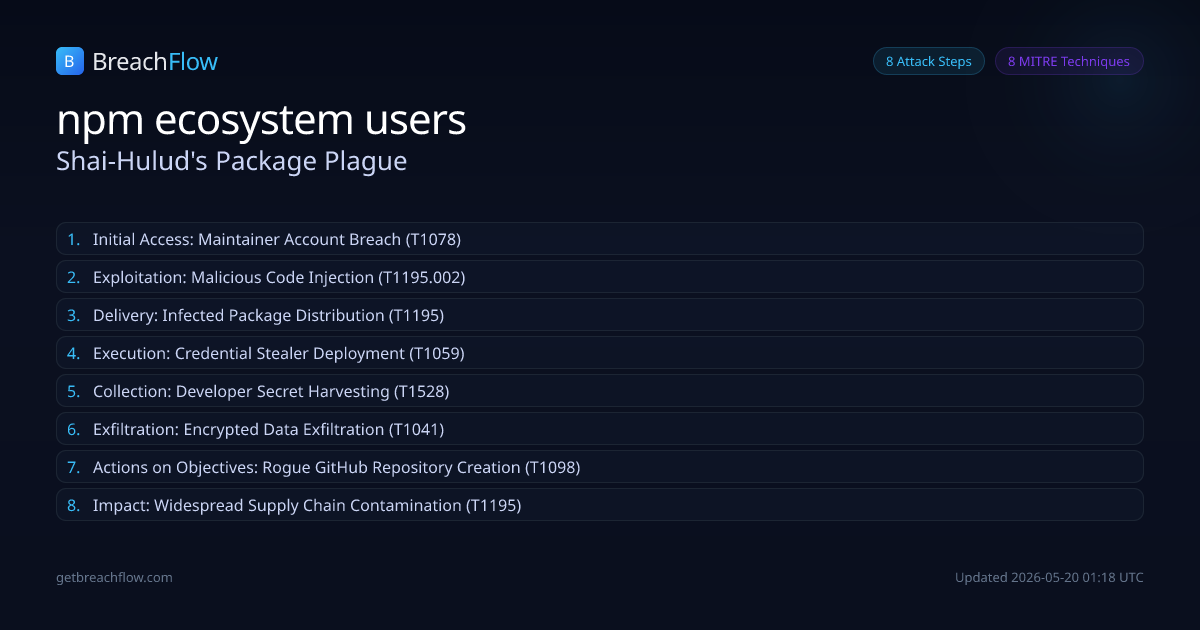
A new Shai-Hulud supply-chain campaign compromised over 600 npm packages, including those in the @antv ecosystem. The malware, injected as an obfuscated 'index.js' payload, steals GitHub, npm, cloud, Kubernetes, Vault, Docker, database, and SSH credentials from developer and CI/CD environments, exfiltrating data via Session P2P and GitHub repositories.
Initial Access
Maintainer Account Breach
confirmed
Threat actors compromised the npm account 'atool', which maintains packages in the @antv namespace, gaining unauthorized access to publish malicious versions.
Defender cut points
Implement strong, phishing-resistant MFA for all npm maintainer accounts.Regularly audit npm account access and permissions.