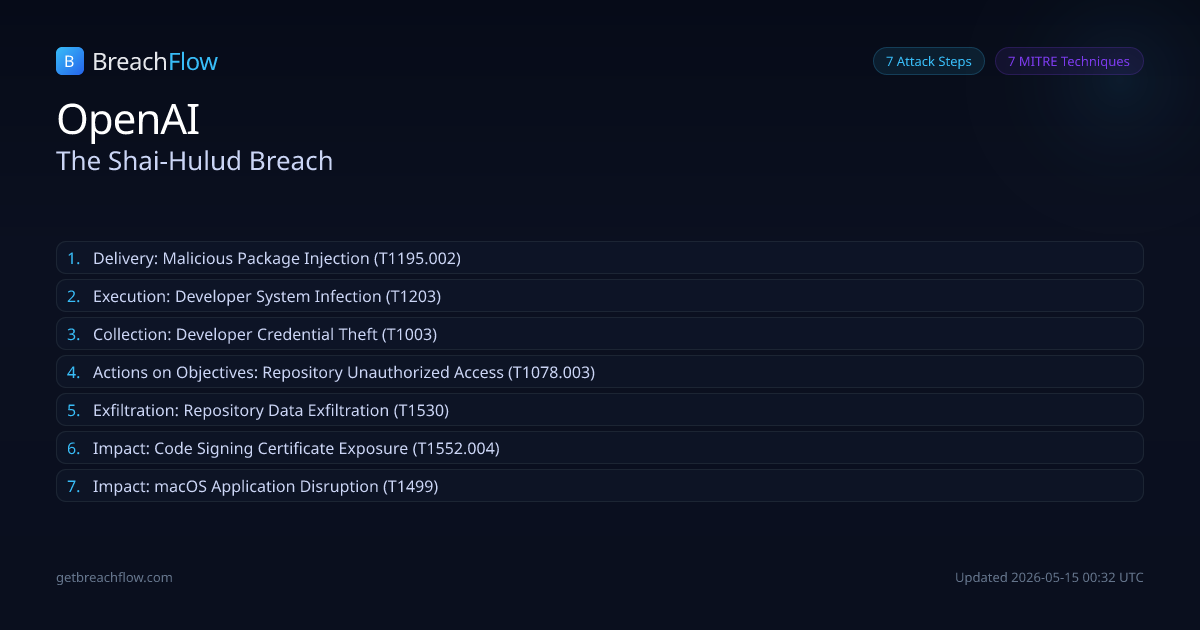
OpenAI confirmed a security breach affecting two employee devices as part of the 'Mini Shai-Hulud' supply-chain campaign by TeamPCP. Attackers gained unauthorized access and exfiltrated limited credentials from internal source code repositories, leading to the rotation of code-signing certificates.
Delivery
Malicious Package Injection
confirmed
The TeamPCP group, in their 'Mini Shai-Hulud' campaign, compromised hundreds of npm and PyPI packages, including those from TanStack and Mistral AI, by abusing GitHub Actions workflows and CI/CD configurations to inject malicious code.
Defender cut points
Implement strict CI/CD pipeline security, including code signing verification and integrity checks for all published packages.Enforce multi-factor authentication and least privilege for CI/CD credentials.