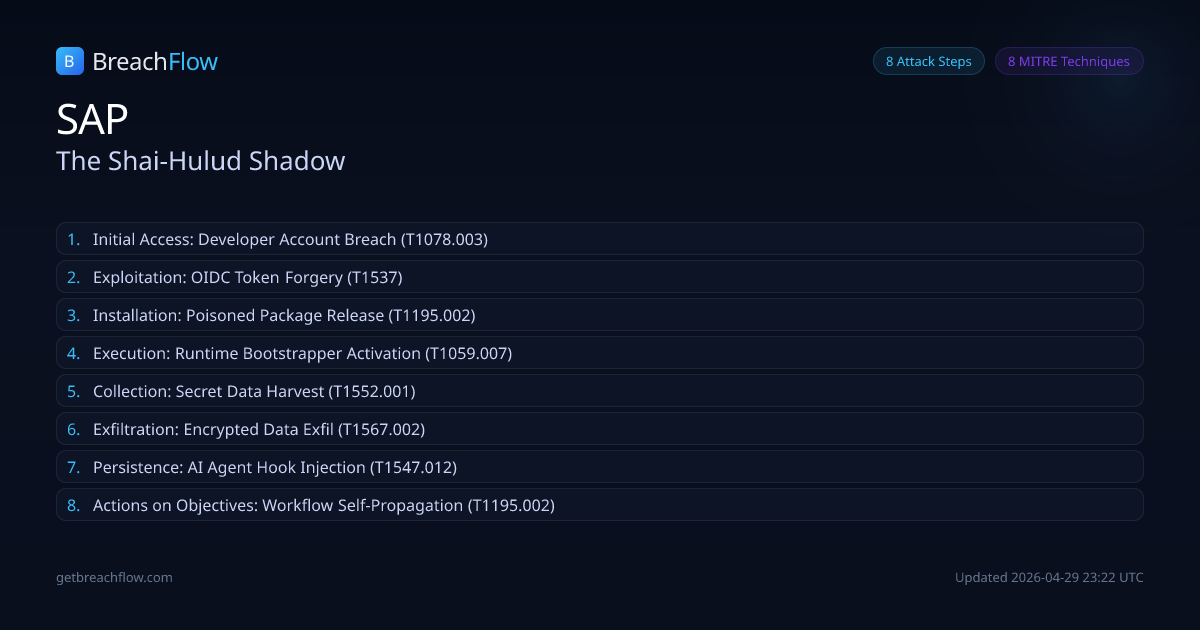
A supply chain attack, dubbed 'mini Shai-Hulud' and linked to TeamPCP, compromised SAP-related npm packages like mbt and @cap-js/*. The attackers injected credential-stealing malware that harvested developer credentials and cloud secrets, exfiltrating them to over 1,100 public GitHub repositories and self-propagating through GitHub Actions workflows.
Initial Access
Developer Account Breach
confirmed
Attackers compromised RoshniNaveenaS's npm account for the @cap-js packages and the 'cloudmtabot' static npm token for the mbt package through an undetermined channel.
Defender cut points
Enforce phishing-resistant FIDO2 MFA on all developer accounts.Regularly rotate and audit static API tokens for suspicious activity.