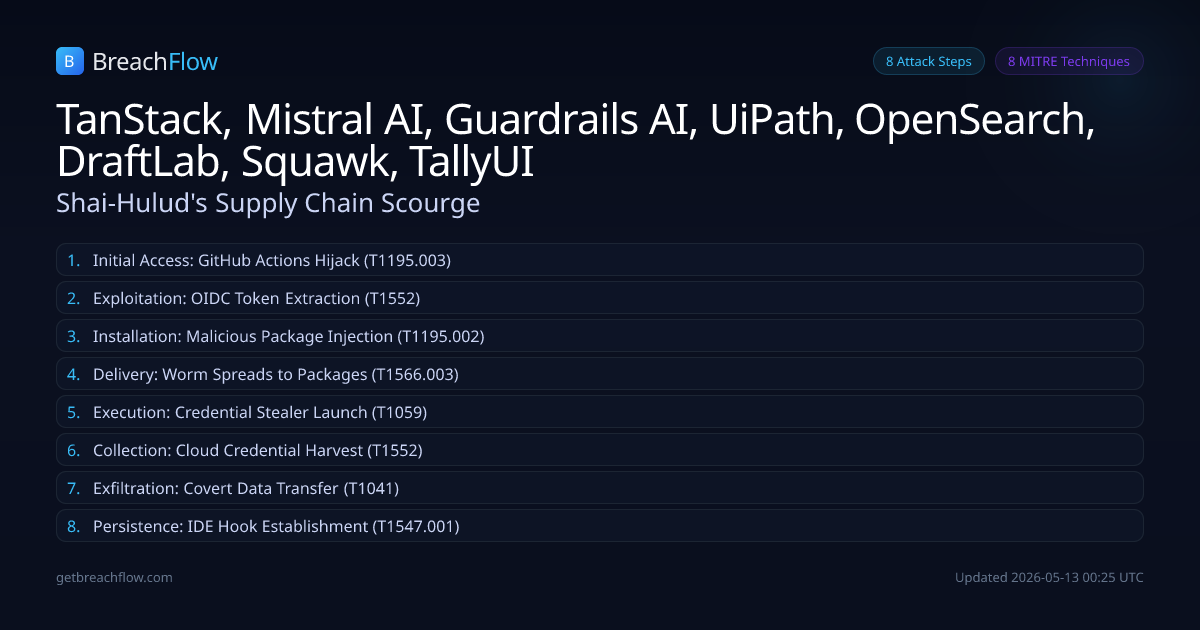
The TeamPCP threat actor deployed the Mini Shai-Hulud worm, compromising over 170 npm and PyPI packages from entities like TanStack, Mistral AI, and UiPath. The malware exfiltrates credentials, GitHub tokens, and repository secrets, and includes a destructive wiper functionality triggered by token revocation.
Initial Access
GitHub Actions Hijack
confirmed
Attackers exploited a chained GitHub Actions attack, leveraging the 'pull_request_target' trigger and cache poisoning to gain control over legitimate workflows within the TanStack project.
Defender cut points
Implement strict OIDC trusted publisher configurations scoped to specific protected branches and workflow files.Regularly audit GitHub Actions workflows for suspicious triggers or dependencies.