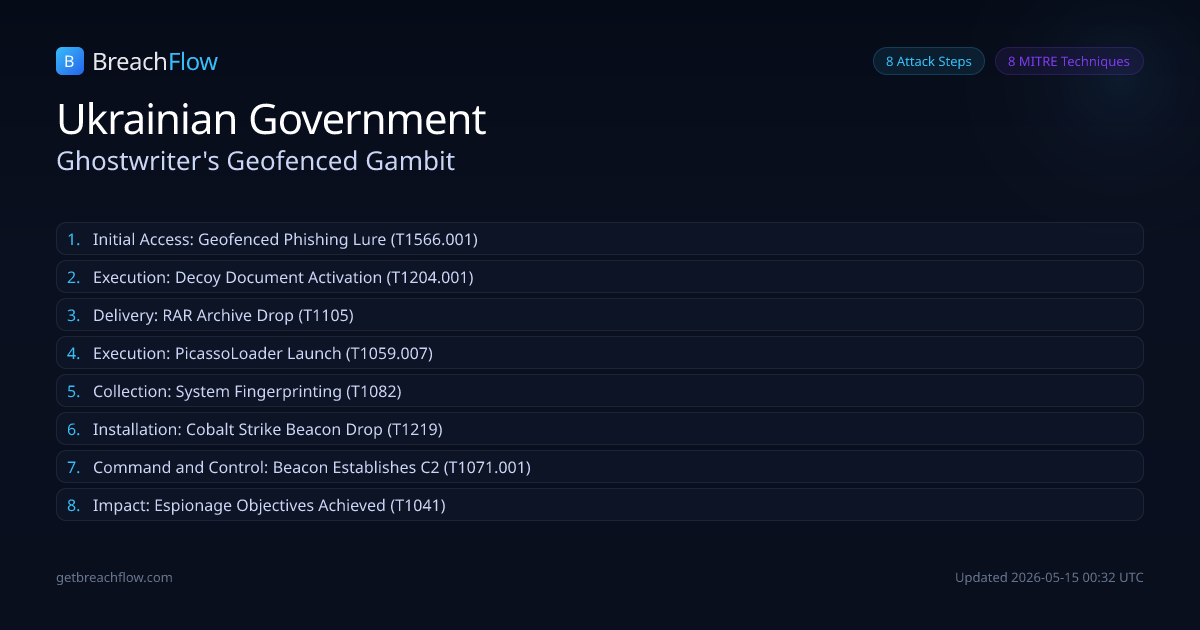
The Belarus-aligned Ghostwriter threat group (also known as FrostyNeighbor, UNC1151) targeted Ukrainian governmental organizations since March 2026 using geofenced PDF spear-phishing. The attack chain deployed a JavaScript version of PicassoLoader for host profiling, ultimately leading to the deployment of Cobalt Strike Beacon.
Initial Access
Geofenced Phishing Lure
confirmed
Ghostwriter initiated attacks by sending spear-phishing emails containing malicious PDF attachments, impersonating the Ukrainian telecommunications company Ukrtelecom, to governmental entities in Ukraine.
Defender cut points
Implement robust email gateway filtering for malicious attachmentsConduct regular user awareness training on phishing threatsUtilize attachment sandboxing for suspicious email attachments